Digital products for founders with an idea and a budget.
From a line to a button.
We build digital products people remember.
A dedicated squad on your project in 72 hours.
Every project starts with guides. Where things belong is measured, not guessed.
We build digital products people remember.
Most projects don't fail at the idea. They fail in between.
One squad. Every layer.
Design, engineering and security under one roof, so nothing gets lost in a handoff.
Pick your pace.
We build for others. And for ourselves.
Numbers we'd rather show than say.
I need a website.
Notes from the build.
 Engineering→
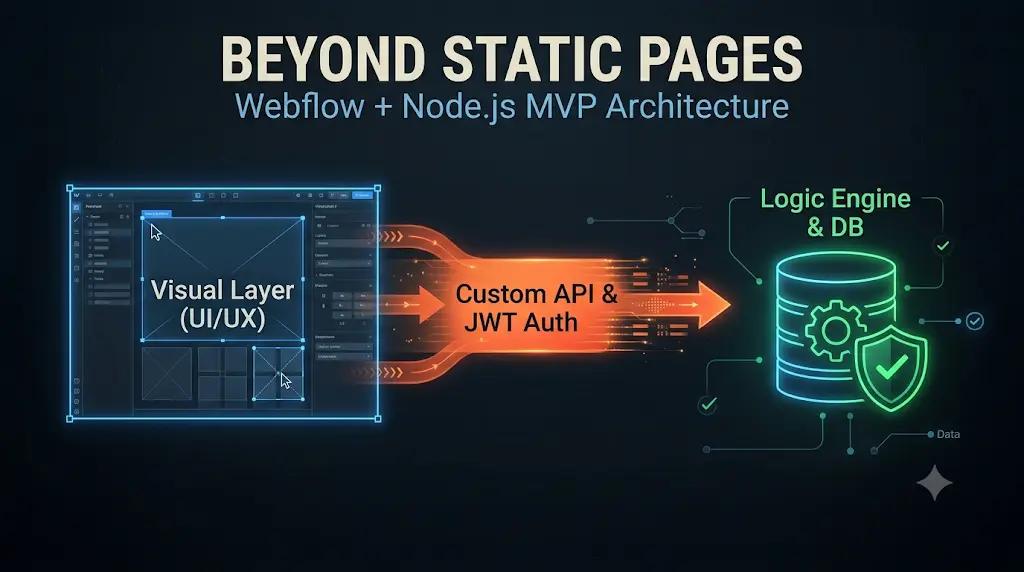
Beyond Static Pages: Architecting a Webflow & Node.js Backend for High-Performance SaaS MVPs
By engineering a hybrid Webflow Node.js SaaS architecture, you can pair the visual perfection of Webflow with a powerful, custom-coded backend engine. Here is the CTO-level playbook on how we bridge visual frontends with headless Node.js APIs to launch high-performance SaaS MVPs in record time. It is a familiar narrative in the modern startup ecosystem. […]
 Agency Growth→
How to Structure White-Label Agency Client Portals for Real-Time Uptime, Security, and Performance Telemetry
Every digital agency managing recurring WordPress care plans eventually hits the Invisible Value Wall. When your WebOps engineering team performs flawlessly updating 30+ plugins seamlessly, blocking brute-force attacks at the edge, running automated visual regression tests, and maintaining 99.99% uptime nothing breaks. And when nothing breaks for six consecutive months, the client’s CFO reviews the […]
 SiteOps→
Enterprise Security Hardening: Implementing Zero-Trust Administrator Access and Passkey Authentication on WordPress
Over 80% of successful WordPress compromises do not stem from sophisticated zero-day exploits in server operating systems. They stem from broken authentication: Stolen administrator credentials harvested from third-party database breaches. Credential stuffing and distributed brute-force botnets assaulting /wp-login.php and xmlrpc.php. Phishing attacks that successfully intercept traditional Time-based One-Time Password (TOTP) codes or SMS two-factor authentication […]